
NSE 6 Network Security Specialist Certified Official Practice Test NSE6_FSR-7.3 - Sep-2026
Ace Fortinet NSE6_FSR-7.3 Certification with Actual Questions Sep 30, 2026 Updated
NEW QUESTION # 13
When configuring an HA cluster with an externalized PostgreSQL database, which two tiles on the database server need to be configured to trust all FortiSOAR nodes' incoming connections? (Choose two.)
- A. db_external_config.yml.
- B. pg_hba.conf
- C. db_config.yml
- D. postgreaq1.conf
Answer: B,D
Explanation:
In a FortiSOAR High Availability (HA) cluster setup with an externalized PostgreSQL database, it is necessary to configure the database server to allow incoming connections from all FortiSOAR nodes. This configuration involves modifying the pg_hba.conf file to set up host-based authentication and control which IP addresses can connect. The postgresql.conf file must also be adjusted to enable listening on all necessary IP addresses, which is critical for FortiSOAR nodes to connect to the database server securely and reliably. Together, these configurations ensure that all FortiSOAR nodes can access the database, facilitating effective HA functionality.
NEW QUESTION # 14
Which two ports must be open between FortiSOAR HA nodes'* (Choose two.)
- A. Port 6380
- B. Port 9200
- C. Port 25
- D. Port 5432
Answer: B,D
Explanation:
In a FortiSOAR HA configuration, certain ports must be open for communication between nodes. Port 5432 is required for PostgreSQL database communication, which is essential for data replication between HA nodes. Port 9200 is used by Elasticsearch, which FortiSOAR leverages for indexing and search functions across the nodes. These ports must be accessible between nodes to ensure seamless operation and data consistency within the cluster.
NEW QUESTION # 15
Which SMS vendor does FortiSOAR support for two-factor authentication?
- A. Google Authenticator
- B. Twilio
- C. Telesign
- D. 2factor
Answer: C
Explanation:
For two-factor authentication (2FA) via SMS, FortiSOAR supports integration with Telesign. This vendor provides SMS-based 2FA services, enabling FortiSOAR to leverage Telesign's API for sending verification codes as part of its security features. Telesign's service is compatible with FortiSOAR, ensuring secure user authentication when accessing the platform or certain features.
NEW QUESTION # 16
For which two modules on FortiSOAR can you create SLA templates7 (Choose two.)
- A. Incidents
- B. Alerts
- C. Tasks
- D. Indicators
Answer: A,C
Explanation:
Explanation:
SLA templates can be created for incidents to track and manage the resolution time for various types of incidents, ensuring that they are addressed within the defined timeframes.
SLA templates can also be applied to tasks to monitor and manage their completion time, helping to maintain efficiency and accountability within workflows.
NEW QUESTION # 17
An administrator is issuing the following command on a node trying to join a FortiSOAR duster as a standby:
csadm ha join-cluster --status active -role secondary --primary-node 10.0.1.160 The node fails to join the cluster. What is the issue?
- A. The role value should be worker.
- B. The status value should be passive.
- C. The IP address should be for secondary-node Instead of primary-node.
- D. The primary node needs to be resolvable via FQDN.
Answer: B
Explanation:
When joining a FortiSOAR cluster as a standby node, the correct status value should be passive. Using active would imply that the node is trying to join as an active node, which could cause conflicts in the cluster setup.
In FortiSOAR, standby nodes must be set as passive to ensure they are recognized correctly and to avoid conflicts with the primary node or other active nodes within the cluster. Therefore, setting the status to passive will resolve the issue and allow the node to join the cluster as intended.
NEW QUESTION # 18
Which CLI command adds the hostnames of the secondary nodes to the active primary node's permitted list?
- A. csadm ha allowlist
- B. csadm ha list-nodes --active
- C. csadm ha list-nodes -active --secondary
- D. csadm ha export-conf
Answer: A
Explanation:
The command is specifically used to add the hostnames of secondary nodes to the active primary node's permitted list, enabling them to join and communicate within the HA cluster.
NEW QUESTION # 19
Refer to the exhibit. How long after the syops-ha service goes down will the heartbeat missed notification be sent to the administrator?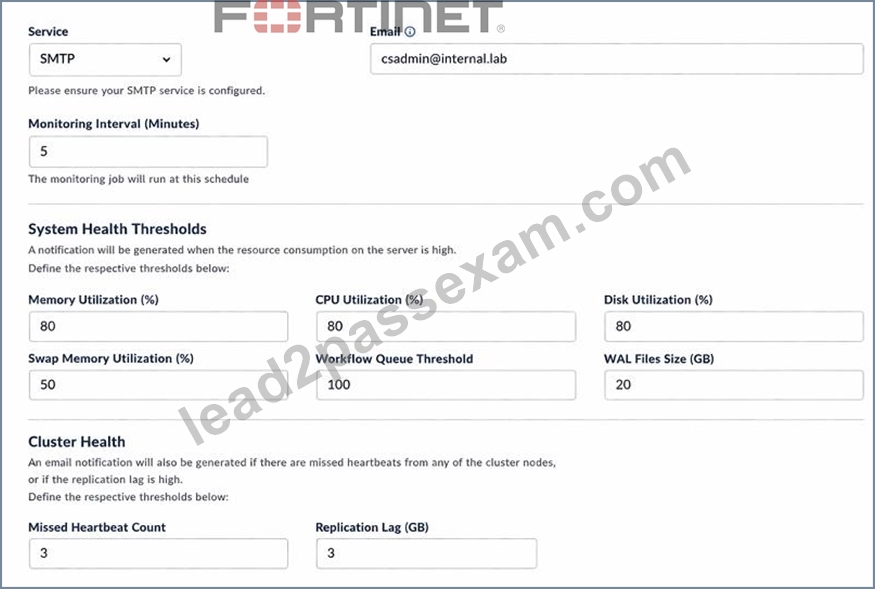
- A. 5 minutes
- B. 60 minutes
- C. 15 minutes
- D. 3 minutes
Answer: C
Explanation:
If you set the Monitoring Interval to 5 minutes and the missed Heartbeat Count to 3, this means that when the heartbeat is missed and the cyups-ha services is down for the last 15 minutes or more the notification will be sent.
NEW QUESTION # 20
When deleting a user account on FortiSOAR, you must enter the user ID in which file on FortiSOAR?
- A. config_yml
- B. userDelete.txt.
- C. usersToDelete.txt
- D. scripts
Answer: C
Explanation:
When deleting a user account in FortiSOAR, the user ID must be entered into the usersToDelete.txt file. This file is specifically used to list users that are marked for deletion. Once the user IDs are listed in this file, the system can process the deletion of these accounts as part of its user management operations. This method ensures that only specified users are deleted, as referenced in FortiSOAR's administrative controls.
NEW QUESTION # 21
Which three activities can be achieved using the FortiSOAR queue and shift management feature? (Choose three)
- A. Designate a coordinator to monitor queues and shifts
- B. Create queue rules based on matching conditions
- C. Generate shift leads and shift members
- D. Set up queue meeting rooms
- E. Initiate shift handovers
Answer: B,C,E
Explanation:
The FortiSOAR queue and shift management feature enables several key activities for managing shifts and queues. Administrators can initiate shift handovers, allowing for smooth transitions between shift leads and members. They can also designate specific roles within shifts, including shift leads and members, to define responsibilities. Additionally, queue rules can be established based on certain conditions, ensuring that incidents and tasks are assigned according to predefined criteria, which helps streamline operations and improve response times.
NEW QUESTION # 22
Which three roles are defined as SAML roles? (Choose three.)
- A. Attribute map
- B. Service provider
- C. Identity provider
- D. Principal
- E. Role
Answer: B,C,D
NEW QUESTION # 23
Which three items are backed up when you run the csadmin db --backupcommand on FortiSOAR? (Choose three.)
- A. Site packages
- B. The pg_hba.conffile
- C. System logs
- D. Connectors
- E. Licensing
Answer: A,D,E
Explanation:
The csadmin db --backup command backs up the FortiSOAR database content, which includes site packages, connectors, and licensing information stored within the database.
NEW QUESTION # 24 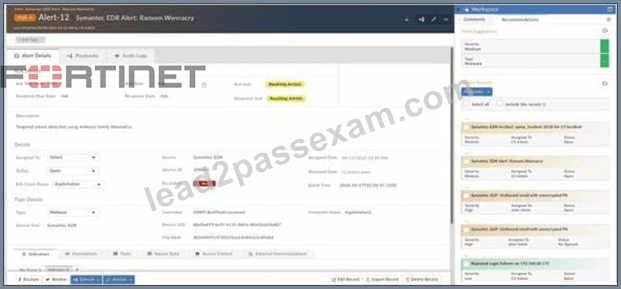
View the exhibit. The dataset on FortiSOAR has been trained to predict which record field?
- A. Assigned To
- B. Playbooks
- C. Status
- D. Severity
Answer: D
NEW QUESTION # 25
What are two system-level logs that can be purged using application configuration? (Choose two.)
- A. Reporting logs
- B. Audit togs
- C. Executed Playbook logs
- D. Connector logs
Answer: B,C
Explanation:
In FortiSOAR, system-level logs that can be purged include both "Audit logs" and "Executed Playbook logs." These types of logs can be configured to be purged periodically to free up storage space and ensure that unnecessary logs do not impact system performance. The application configuration allows administrators to schedule automatic purges, which can be especially useful in high-activity environments where log data accumulates quickly. Purging these logs helps maintain a cleaner and more efficient system.
NEW QUESTION # 26
Which two system monitoring reports are available on the System Monitoring widget? (Choose two.)
- A. Playbook Health Status
- B. CPU Usage
- C. Service Status
- D. RAM Usage
Answer: B,C
NEW QUESTION # 27
A security analyst has reported unauthorized access to System Configuration. You must review the user's current level of access, and then restrict their access according to your organization's requirements. As part of your auditing process, which two actions should you perform? (Choose two.)
- A. Remove all record ownership that is assigned to the user.
- B. Review the user's learn hierarchy to ensure that the appropriate relationships are configured.
- C. View the user's effective role permissions, and then investigate which role is providing that access.
- D. Remove the create, read, update, and delete (CRUD) permissions or roles that the user does not require.
Answer: B,C
Explanation:
To audit and restrict a user's access within FortiSOAR, particularly in response to unauthorized access reports, it's necessary to review the user's effective role permissions. This involves checking which roles grant the user access to the System Configuration module and adjusting as needed. Additionally, reviewing the user's team hierarchy ensures that the user's access aligns with the organization's policies. Misconfigurations in team relationships can sometimes inadvertently provide elevated access; hence, confirming that the team setup is correct is a critical part of the auditing process.
NEW QUESTION # 28
Refer to the exhibit. Which statement correctly describes the user's login behavior?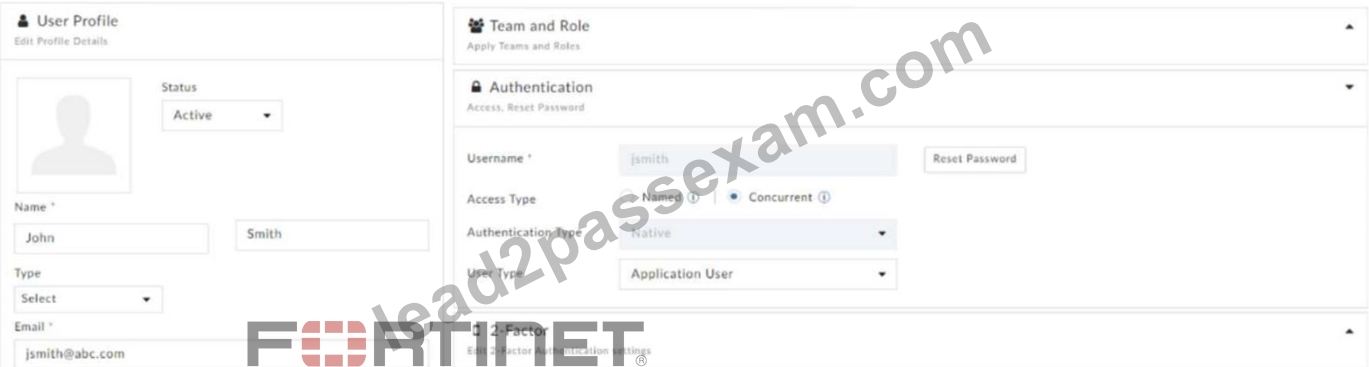
- A. The user can log in only if there are enough seats available.
- B. The user is sent to a waiting queue if there are named users logged in.
- C. The user has an active concurrent session that does not time out.
- D. The user will always be able to draw from the concurrent pool and log in.
Answer: A
Explanation:
In FortiSOAR, when a user is configured with "Concurrent" access type, their ability to log in depends on the availability of concurrent user seats. This means the user can only log in if there are available seats in the concurrent pool. If all seats are occupied, the user must wait until a seat becomes free. This configuration allows multiple users to share a pool of licenses, making it suitable for environments where not all users need constant access.
NEW QUESTION # 29
Which three features are installed with the FortiSOAR Incidence Response Content Pack?
(Choose three answers)
- A. Sample data for playbooks
- B. System monitoring connectors
- C. System playbooks
- D. SLA template module
- E. Sample alerts and incidents
Answer: A,C,E
Explanation:
Sample Alerts and Incidents (C): The content pack includes a set of demo records. Upon installation and clicking the "Demo IR Records" button, the system populates the Alerts and Incidents modules with pre-configured samples, including associated indicators and assets, to demonstrate how records are handled.
System Playbooks (D): It installs a comprehensive collection of "out-of-the-box" (OOB) playbooks. These include system-level playbooks used for triaging, indicator extraction, and managing standard record lifecycles (such as auto-populating dates when a record is closed).
Sample Data for Playbooks (B): Along with the records themselves, the pack includes simulation and training data (often referred to as "Playbook Samples" or "Mock Data"). This allows administrators to test playbook logic and workflows without requiring live feeds from third-party security tools.
NEW QUESTION # 30
Which service on FortiSOAR in the playbook scheduler?
- A. celerybeatd
- B. uwsgi
- C. celeryd
- D. cyops-tomcat
Answer: A
Explanation:
The celerybeatd service in FortiSOAR is responsible for the playbook scheduler. It handles the periodic execution of scheduled playbooks by managing tasks that need to be executed at specific times or intervals. This service works in conjunction with the Celery worker processes (celeryd) to execute the scheduled tasks.
NEW QUESTION # 31
View the exhibit. What does the command output mean?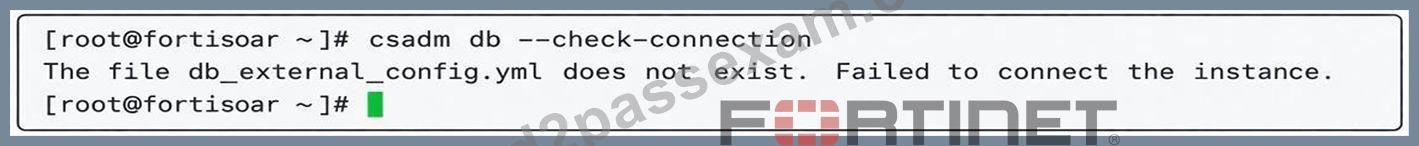
- A. There is no connectivity between the PostgreSQL databases of the primary and secondary FortiSOAR instances.
- B. The configuration to enable database externalization has not been completed.
- C. The local PostgreSQL database is configured on the FortiSOAR instance.
- D. The local PostgreSQL database is disabled on the FortiSOAR instance.
Answer: B
NEW QUESTION # 32
Which two statements about FortiSOAR virtual instance deployment requirements are true?
(Choose two.)
- A. FortiSOAR Cloud is a subscription service that allows you to deploy an instance hosted on FortlCloud.
- B. While memory and storage can be added based on requirements, charges are required for every vCPU that is added to the FortiSOAR VM.
- C. There are size limits for the records database, but no charges or fees for storing months or years worth of data.
- D. FortiSOAR is supported on VMWare ESXi and Amazon Web Services (AWS).
Answer: A,D
Explanation:
FortiSOAR offers flexibility in deployment environments, including FortiSOAR Cloud, which is a subscription service that enables hosting on FortiCloud. This provides cloud-hosted management with scalable resources. Additionally, FortiSOAR supports deployment on VMware ESXi and Amazon Web Services (AWS), allowing organizations to choose based on their infrastructure preferences. This flexibility ensures that FortiSOAR can be integrated into various IT environments depending on business needs.
NEW QUESTION # 33
A security analyst has reported unauthorized access to System Configuration. You must review the user's current level of access, and then restrict their access according to your organization's requirements. As part of your auditing process, which two actions should you perform? (Choose two.)
- A. Remove all record ownership that is assigned to the user.
- B. View the user's effective role permissions, and then investigate which role is providing that access.
- C. Remove the create, read, update, and delete (CRUD) permissions or roles that the user does not require.
- D. Review the user's learn hierarchy to ensure that the appropriate relationships are configured.
Answer: B,C
Explanation:
Explanation:
Reviewing and restricting CRUD permissions ensures that users only have access to the specific resources they need to perform their tasks, adhering to the principle of least privilege.
By reviewing the user's effective role permissions, you can identify the source of unauthorized access and take appropriate steps to adjust or remove the roles causing the issue.
NEW QUESTION # 34
Which three roles are defined as SAML roles?
(Choose three.)
- A. Attribute map
- B. Service provider
- C. Identity provider
- D. Principal
- E. Role
Answer: B,C,D
NEW QUESTION # 35
Which two options can you use to configure FortiSOAR proxy? (Choose two.)
- A. Configure a schedule to forward traffic to a proxy only during certain hours.
- B. Define multiple proxy URLs for each protocol.
- C. Add environment variables and set up proxies or protocols other than HTTP and HTTPS.
- D. Define a list of addresses that do not need to be routed through a proxy server.
Answer: C,D
Explanation:
FortiSOAR proxy configuration allows defining exceptions so specific addresses bypass the proxy, and it supports using environment variables to configure proxies, including for protocols beyond HTTP and HTTPS.
NEW QUESTION # 36
......
Fortinet NSE6_FSR-7.3 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
Try Free and Start Using Realistic Verified NSE6_FSR-7.3 Dumps Instantly.: https://www.lead2passexam.com/Fortinet/valid-NSE6_FSR-7.3-exam-dumps.html
2026 The Most Effective NSE6_FSR-7.3 with 75 Questions Answers: https://drive.google.com/open?id=1KuNc-9EPcrfqj-uxKa-dFbrkHg0IoaKA